
For years, compliance software mostly helped people store documents, search policies, track tasks, and build reports. It made compliance teams more organized, but it did not remove much of the work itself. A person still had to read the new rule, decide what changed, find the right policy, ask different teams for evidence, check whether a control worked, write the report, and chase people when something was missing.
AI agents could change that model.
A compliance agent can watch a regulatory source, detect a change, compare the new language with a company’s existing controls, find affected policies, collect supporting evidence from internal systems, create a review package, route the issue to the right person, and track the response. The human compliance officer still makes important decisions. The difference is that much of the work around that decision can happen automatically.
That shift matters in New York because companies here often sit inside several regulatory systems at the same time. A Manhattan financial firm may answer to the Securities and Exchange Commission, FINRA, the New York State Department of Financial Services, federal anti-money-laundering rules, New York cybersecurity rules, employment laws, privacy requirements, and internal global standards. A large employer can also face New York City rules covering automated employment decision tools.
The regulatory environment is still moving. On September 10, 2026, for example, New York DFS published fresh guidance explaining how regulated companies should conduct and use the risk assessments required by its cybersecurity regulation. DFS said assessments need a repeatable method, proper scope, documented links between risks and controls, regular updates, and clear governance. It also specifically listed artificial intelligence as an emerging technology that may create a material change in cyber risk. (Department of Financial Services)
That is a good example of why the next generation of compliance technology will probably not be another search box.
It will be a system that can notice something changed and start doing the work.
The Short Version: Compliance AI Is Moving From Finding Rules to Completing Work
The first wave of generative AI inside compliance departments focused on questions.
“What does this policy say?”
“Summarize this regulation.”
“What records do we need?”
“Explain this enforcement action.”
Those uses can save time, but they leave the operating model mostly unchanged. An employee asks a question, receives an answer, and then goes back to the old workflow.
An AI compliance agent is different because it can move through several steps without requiring a new prompt for every step.
Imagine that a regulator publishes updated cybersecurity guidance. A properly designed compliance agent could identify the document, compare it with the earlier version, classify the affected obligations, search the company’s risk register, locate related controls, pull recent testing evidence, identify gaps, draft proposed remediation tasks, and send the package to a named compliance owner.
That is not simply better search.
It is workflow automation with reasoning in the middle.
| Traditional compliance assistant | Compliance agent |
| Answers a question | Watches for events |
| Summarizes a rule | Maps the rule to obligations |
| Finds a policy | Checks whether the policy matches the obligation |
| Drafts a checklist | Starts and tracks the checklist |
| Explains evidence requirements | Collects available evidence |
| Waits for another prompt | Continues through approved steps |
| Produces text | Produces a traceable work record |
| Helps the compliance officer | Works inside the compliance process |
FINRA is already discussing this shift directly. Its 2026 Regulatory Oversight Report describes AI agents as systems able to perform and complete tasks on behalf of users and warns firms about autonomy, authority, auditability, data sensitivity, weak domain knowledge, and the need for human oversight and guardrails. (FINRA)
That combination—more automation plus more control—is the central idea behind compliance agents.
Why New York Is Becoming an Important Test Market for Compliance Agents
New York is a useful place to study this technology because the state does not have one simple AI compliance regime.
It has overlapping systems.
New York City regulates some automated hiring tools. DFS regulates banks, insurers, virtual-currency companies, and other financial firms. Public companies and securities businesses face SEC and FINRA requirements. General consumer-protection laws still apply when businesses use AI. Cybersecurity and breach-notification requirements add another layer.
New York has also begun creating rules aimed directly at advanced AI.
The RAISE Act, signed in December 2025, created transparency and safety obligations for covered frontier-model developers, including requirements around safety information and reporting certain critical incidents. The state also created an oversight function connected to DFS. (Governor Kathy Hochul)
At the same time, New York regulators continue to make an important point: companies do not get a regulatory exception because they use AI.
DFS has said that existing laws continue to apply to new technologies, while FINRA has repeatedly stressed that its rules are technology neutral. The SEC also withdrew its proposed predictive-data-analytics conflict rules in June 2025, which makes it especially important not to confuse proposed AI-specific rules with requirements that are actually in force. Existing securities obligations around supervision, fraud, communications, records, disclosures, and cybersecurity still matter. (Department of Financial Services)
This creates an unusual situation.
The number of documents that mention AI may be growing quickly, but the hardest compliance work often comes from connecting AI activity to rules that never mention AI at all.
That is exactly the type of problem agents may be good at solving.
Original Research: What 15 Public Regulatory Sources Say About the Compliance Controls That Matter
To test where AI compliance agents could create the most value, NYC Tech Journal conducted an original structured review of 15 public regulatory, enforcement, and risk-management sources relevant to companies operating in New York.
The analysis was completed using sources available as of September 11, 2026.
How We Built the Dataset
We selected sources only when they met at least one of three conditions. They directly applied to New York companies, showed how a major regulator was applying existing rules to AI or technology, or provided a widely used public framework for managing AI risk.
The corpus included binding rules, regulatory guidance, enforcement examples, and voluntary standards. Those categories do not have the same legal force, so we did not calculate a “legal requirement score.” Instead, we measured how often eight operating controls appeared clearly in the source material.
Each source received a binary score of 1 when a control was explicitly required, recommended, expected, or directly highlighted as an important risk-management practice. It received 0 when the control was not clearly present.
The eight controls were:
| Control tested | What counted |
| Inventory and scope | Identifying systems, assets, tools, dependencies, or covered activity |
| Risk assessment and testing | Evaluation, bias testing, control testing, model testing, or formal risk analysis |
| Documentation and traceability | Records linking decisions, risks, controls, evidence, or actions |
| Human oversight | Named accountable people, supervision, board oversight, or human validation |
| Reporting and disclosure | Regulatory reports, notices, public disclosures, escalation, or formal communication |
| Monitoring and incident response | Recurring review, surveillance, logging, alerts, incident response, or reassessment |
| Third-party controls | Vendor due diligence, contracts, supplier monitoring, or downstream risk |
| Fairness and consumer harm | Bias, discrimination, misleading claims, investor harm, or consumer impact |
This is an editorial research model created by NYC Tech Journal. It is designed to find operating patterns, not to replace legal analysis.
The 15-Source Regulatory Corpus
The review included NYC Local Law 144 and its enforcement material; current DFS cybersecurity guidance; DFS AI cybersecurity guidance; DFS third-party guidance; DFS frontier-AI guidance; DFS insurance AI guidance; New York breach requirements; the RAISE Act; SEC cybersecurity disclosure rules; SEC AI-related enforcement; FINRA’s GenAI notice; FINRA’s 2026 agent guidance; FTC AI enforcement; the NIST AI Risk Management Framework; and NIST’s Generative AI Profile. (NYC Homeowner Portal)
Chart 1: How Often Each Control Appeared Across the 15 Sources
Risk assessment / testing 93.3% ███████████████████
Reporting / disclosure 93.3% ███████████████████
Documentation / traceability 86.7% █████████████████
Inventory / scope 80.0% ████████████████
Monitoring / incident response 80.0% ████████████████
Human oversight 66.7% █████████████
Fairness / consumer harm 60.0% ████████████
Third-party controls 53.3% ███████████
| Control | Sources containing signal | Share of sample |
| Risk assessment and testing | 14 of 15 | 93.3% |
| Reporting and disclosure | 14 of 15 | 93.3% |
| Documentation and traceability | 13 of 15 | 86.7% |
| Inventory and scope | 12 of 15 | 80.0% |
| Monitoring and incident response | 12 of 15 | 80.0% |
| Human oversight | 10 of 15 | 66.7% |
| Fairness and consumer harm | 9 of 15 | 60.0% |
| Third-party controls | 8 of 15 | 53.3% |
Finding #1: The Compliance Agent Should Be an Evidence Machine
The most important result is not that regulators care about AI.
It is that they repeatedly care about proof.
Testing and risk assessment appeared in 93.3% of our source sample. Reporting and disclosure also appeared in 93.3%. Documentation appeared in 86.7%, while inventory and monitoring each appeared in 80%.
That pattern suggests that a strong compliance agent should not be designed primarily to “know the law.”
It should be designed to show what the company did about the law.
A weak system might answer, “Your firm should perform a cybersecurity risk assessment.”
A much more useful agent would show when the assessment was last performed, which assets were included, what method was used, which risks were identified, which controls respond to each risk, which evidence supports those controls, what remains unresolved, who accepted residual risk, and when the issue must be reviewed again.
DFS’s September 2026 guidance is unusually clear on this point. It says regulated entities should maintain documentation linking identified risks to specific controls, preserve evidence behind conclusions and management decisions, maintain risk registers or similar tracking systems, and demonstrate how risk assessments influence controls and risk acceptance. (Department of Financial Services)
This leads to a major product design lesson.
The compliance agent of the future may be less like a legal chatbot and more like an automated auditor that never stops organizing evidence.
Original Research: What $89.7 Million of 2025 New York DFS Penalties Tells Us
Regulatory documents tell us what companies should do.
Enforcement actions show what happens when controls fail.
For a second original analysis, NYC Tech Journal reviewed company-level matters described in the New York Department of Financial Services’ 2025 Consumer Protection and Financial Enforcement annual report.
To avoid overstating New York penalty amounts, we excluded multistate settlements when the public report did not clearly separate the amount attributable to New York. That removed the $20 million Bayview multistate settlement and the $4.2 million Wise multistate settlement from our penalty calculation.
We retained 13 company-level matters where a specific DFS or New York penalty amount could be identified from the report.
Table: The 13-Matter DFS Enforcement Sample
| Company or matter | Main issue used in our classification | Penalty used |
| PayPal | Cybersecurity and change-control failures | $2.00M |
| Block | AML and transaction-monitoring failures | $40.00M |
| Roach & Murtha | Debt collection, review and documentation | $0.04M |
| Paxos | KYC, partner oversight and transaction monitoring | $26.50M |
| Healthplex | Cybersecurity, MFA and incident reporting | $2.00M |
| Farmers | Cybersecurity | $2.775M |
| Hagerty | Cybersecurity | $1.85M |
| The Hartford | Cybersecurity | $3.00M |
| Infinity | Cybersecurity and risk assessment | $2.25M |
| Liberty Mutual | Cybersecurity | $2.70M |
| Metromile | Cybersecurity and risk assessment | $2.05M |
| Midvale | Cybersecurity and risk assessment | $2.00M |
| State Auto | Cybersecurity, MFA and monitoring | $2.50M |
| Total | $89.665M |
The underlying DFS report describes the control failures behind these cases, including weak application security, missing or poorly applied policies, delayed incident reporting, inadequate risk assessments, transaction-monitoring backlogs, weak customer due diligence, poor escalation, insufficient access controls, and failures to perform meaningful review. (Department of Financial Services)
Chart 2: Enforcement Frequency and Penalty Dollars Tell Different Stories
SHARE OF THE 13 ENTITIES
Cybersecurity 76.9% ███████████████
AML / financial crime 15.4% ███
Debt collection 7.7% ██
SHARE OF $89.665M PENALTIES
AML / financial crime 74.2% ███████████████
Cybersecurity 25.8% █████
Debt collection <0.1%
This is one of the most useful findings in the research.
Cybersecurity represented 10 of the 13 entities in the sample, or 76.9%. Yet the two AML-related cases represented roughly 74.2% of the penalty dollars because Block and Paxos involved very large penalties.
The median penalty across the 13 matters was $2.25 million. The mean was much higher, about $6.9 million, because the two largest cases heavily pulled the average upward.
Finding #2: Compliance Automation Has Two Different Jobs
The enforcement data points toward two separate problems.
The first is control coverage. Cybersecurity failures appeared again and again across many companies. That means companies need systems that continuously check whether controls exist, whether policies are actually being followed, whether assessments are current, whether access controls are configured correctly, and whether required reports have been filed.
The second problem is high-impact detection.
AML cases were less common in our sample, but the financial effect was far larger. Block’s case involved weaknesses including customer due diligence, risk-based controls, transaction monitoring and a large alert backlog. Paxos faced findings involving partner due diligence, KYC, transaction monitoring, illicit activity and failures to escalate red flags. (Department of Financial Services)
These are ideal areas for AI to assist with volume.
They are terrible areas for uncontrolled AI autonomy.
What an AI Compliance Agent Actually Does
The word “agent” has become so widely used that it can lose meaning.
A compliance agent should not simply be a chatbot with access to regulatory documents. The real value comes from connecting intelligence to controlled action.
Regulatory Change Monitoring
A regulatory monitoring agent watches approved sources such as regulator websites, rule databases, guidance pages and internal legal updates.
When something changes, it should not immediately rewrite company policy.
It should identify the change, preserve the source, timestamp the event, compare new and old language, identify potentially affected obligations, and create a review item.
Consider DFS’s September 10, 2026 risk-assessment guidance. An agent monitoring the DFS industry-letter page could have detected the new publication, identified phrases dealing with annual updates, asset inventory, emerging technologies, third parties, traceability and risk acceptance, and matched those concepts against an existing control library. (Department of Financial Services)
The final interpretation would still belong to legal or compliance staff.
The machine’s job is to make sure the change is seen and prepared for review.
Obligation Mapping
Rules are written as documents.
Companies operate through systems.
That gap creates enormous amounts of compliance work.
An obligation-mapping agent converts regulatory language into structured requirements such as responsible owner, affected entity, relevant business process, required evidence, deadline, testing frequency, exception rule and reporting trigger.
The result might look like this:
| Regulatory requirement | Internal control | Evidence | Owner |
| Annual cyber risk assessment | Enterprise cyber-risk review | Approved assessment | CISO |
| Update after material technology change | Change-trigger review | Change ticket + assessment | Security risk |
| Maintain current asset inventory | Asset-management control | Current inventory export | IT |
| Assess third-party exposure | Vendor-risk control | Vendor assessment | Procurement/risk |
| Document risk acceptance | Risk acceptance process | Approval record | Risk owner |
| Report qualifying event | Incident-response process | Filing + timestamp | Legal/CISO |
The value is not the table itself.
The value comes when every row remains connected to live evidence.
Evidence Collection
This may become the largest near-term opportunity.
Compliance teams spend huge amounts of time asking for screenshots, tickets, reports, logs, approvals, training records, vendor documents, audit results and policy versions.
An agent can collect much of this automatically.
If a company claims privileged accounts are reviewed quarterly, the agent could retrieve the account export, compare it with the approved access list, confirm review completion, identify unmatched accounts and place the evidence into the correct audit period.
If a policy says a vendor assessment must occur annually, the agent can find the latest assessment and calculate whether it is still current.
If evidence is missing, it can open a task instead of pretending the control passed.
That last rule is critical.
A trustworthy compliance agent must be allowed to say, “I cannot prove this.”
The Best Compliance Agents Will Know the Difference Between a Rule and Evidence
This distinction sounds simple.
It is not.
A rule might say an organization must maintain a risk-based cybersecurity program. A policy might say the organization reviews access quarterly. A ticket might show a review was requested. A signed approval might show the review was completed.
Those are four different things.
Poorly designed AI systems can combine them into one confident answer.
A regulator will not.
This is why every compliance agent should work with an evidence hierarchy.
A Practical Evidence Hierarchy
| Level | Example | Strength |
| 1 | Regulation, statute or regulator order | Authoritative obligation |
| 2 | Regulator guidance | Supervisory expectation or interpretation |
| 3 | Internal approved policy | Company commitment |
| 4 | Approved control procedure | How requirement should be met |
| 5 | System evidence | What actually happened |
| 6 | Human statement | Supporting information, but weaker |
| 7 | AI inference | Useful for analysis, never proof by itself |
An agent should never present Level 7 as Level 5.
That sounds obvious, but it may be one of the most important compliance-agent design principles.
New York City Hiring Shows Why Continuous Compliance Is Hard
NYC Local Law 144 provides one of the clearest examples of a compliance workflow that can be structured.
Employers and employment agencies using covered automated employment decision tools need a recent bias audit, public information about that audit and required notices. The city says the bias audit must have occurred within one year before use of the tool. (NYC Homeowner Portal)
A static checklist can help once.
An agent can manage the lifecycle.
It can maintain the inventory of hiring tools, store the date each tool entered use, track the latest audit date, monitor whether public disclosures remain accessible, check notification templates, flag tools approaching the one-year audit limit and create a review when a vendor changes its model.
That is much closer to the real compliance problem.
The Enforcement Gap Makes Automation More Interesting
A New York State Comptroller audit published in December 2025 reviewed NYC’s enforcement of Local Law 144.
The audit found that DCWP had received only two AEDT complaints during the review period. DCWP reviewed websites and bias audits of 32 companies and identified one issue, while the Comptroller’s review of the same companies found at least 17 instances of potential non-compliance. (Office of the State Comptroller)
It would be wrong to treat those 17 instances as proof that 17 of 32 companies broke the law. The report does not make that claim.
But it does show something important for compliance design.
Visibility is difficult.
A company cannot assume that low enforcement activity means its internal process is strong.
A compliance agent should therefore be designed around the obligation itself, not around the odds of getting caught.
DFS Cybersecurity Rules Are Almost Built for Agent-Based Evidence Management
The New York DFS cybersecurity regime offers another strong use case because many requirements are recurring.
The current risk-assessment guidance says regulated entities should use a defined and repeatable method, maintain an accurate asset inventory, include third-party and emerging risks, document the links between risks and controls, and update assessments at least annually and when material business or technology changes affect cyber risk. (Department of Financial Services)
That creates event-driven compliance.
Instead of telling a team, “Remember to revisit the risk assessment when something important changes,” the system can watch for the kinds of events that should start a review.
A large cloud migration could trigger one.
A merger could trigger one.
A major outsourcing deal could trigger one.
Deployment of a new AI system could trigger one.
A material vendor incident could trigger one.
DFS even says major technology developments such as frontier AI models may require an updated assessment when they materially change a covered entity’s cyber risk. (Department of Financial Services)
This is an important shift in how companies should think about compliance automation.
The best trigger may not be a date.
It may be an event.
Third-Party AI Risk Could Become One of the Largest Agent Opportunities
Modern companies do not build everything themselves.
They depend on cloud companies, data providers, software vendors, payment systems, model providers, consultants and outside service firms.
That means compliance increasingly depends on people outside the company.
DFS’s October 2025 third-party guidance says covered entities should take a risk-based approach across vendor selection, due diligence, contracting, ongoing monitoring and termination. The guidance discusses access controls, data protection, incident notification, subcontractors, audit trails, AI use, data-location issues and continued assessment. (Department of Financial Services)
This is a natural agent workflow.
A Vendor Compliance Agent Could Run the Entire Review Cycle
When a new vendor request arrives, the agent could classify the vendor based on data access, system access and business criticality.
It could send the correct questionnaire, read the response, identify missing answers, compare provided security information with company standards, check whether supporting documents are current and create follow-up questions.
It could then review the proposed contract against approved clauses.
If the vendor will use AI, the agent could check whether the contract explains how company data can be used, whether data may be used for model training, which subprocessors may receive it and what happens when the relationship ends.
After approval, the agent can schedule the next review automatically.
That is a much larger opportunity than simply asking ChatGPT to summarize a SOC 2 report.
Frontier AI Is Also Changing the Cyber Risk That Compliance Teams Must Monitor
Compliance agents do not only have to control internal AI.
They also have to respond to risks created by better AI systems outside the company.
In May 2026, DFS warned regulated companies that more capable frontier models could increase the speed and scale at which attackers identify and exploit vulnerabilities. The department recommended refreshed risk assessments, faster vulnerability management, stronger third-party dependency mapping, better monitoring and additional human validation for AI-generated code. (Department of Financial Services)
That creates a useful feedback loop.
AI increases compliance complexity.
AI may also help companies manage that complexity.
A vulnerability-management agent, for example, could monitor vulnerability feeds, match affected software against the company asset inventory, combine severity with business criticality, identify exposed systems, start remediation workflows and track overdue fixes.
The agent should not autonomously patch critical production systems without controls.
Its real value is making sure nothing disappears between discovery and remediation.
Insurance Shows What Mature AI Governance May Look Like
New York insurers face some of the clearest state-level guidance on AI decision systems.
DFS’s 2024 insurance circular letter addresses AI systems and external consumer data used in underwriting and pricing. It focuses on areas including fairness, governance, risk management, transparency and vendor oversight.
DFS also says insurers remain responsible for outcomes when third-party AI systems are used. The circular describes assessments for disproportionate adverse effects and allows examinations of insurers’ AI use. (Department of Financial Services)
This is important because it shows the difference between “AI policy” and an operating AI governance system.
An insurer needs to know which models exist.
It needs to know where they are used.
It needs to know what data each model consumes.
It needs to know which customers can be affected.
It needs testing evidence.
It needs change history.
It needs vendor information.
It needs evidence of governance.
It needs a way to investigate unexpected outcomes.
A compliance agent can keep those pieces connected.
Securities Firms Cannot Treat the AI Agent as an Unsupervised Employee
FINRA may offer the clearest warning for Wall Street.
Its 2024 GenAI notice says existing rules continue to apply when firms use generative AI. If AI is used as part of a supervisory system, firms should address areas such as technology governance, model risk, privacy, data integrity, reliability and accuracy. FINRA also says firms should evaluate AI tools before deployment, including third-party technology. (FINRA)
By 2026, FINRA was talking specifically about agents.
Its concerns include agents acting without human approval, operating outside their intended authority, creating difficult-to-audit workflows, mishandling sensitive information and lacking enough specialized knowledge for complex financial tasks. FINRA suggests firms consider monitoring agent access and data handling, deciding where humans need to remain in the loop, recording actions and decisions, and creating guardrails that restrict behavior. (FINRA)
That should shape the architecture.
The compliance agent should not have the permissions of the chief compliance officer.
It should have the minimum permissions needed for its task.
AI-Washing Turns Marketing Claims Into Compliance Data
One overlooked compliance-agent use case is marketing.
The SEC has already brought enforcement actions involving false or misleading statements about firms’ use of AI. In 2024, two investment advisers agreed to pay a combined $400,000 to settle charges involving misleading AI claims. (SEC)
The FTC has taken similar action against deceptive AI claims and AI-enabled schemes through its Operation AI Comply enforcement effort. (Federal Trade Commission)
This creates a simple rule for companies.
Every important AI claim should have evidence.
If the website says a product uses AI to improve accuracy, what test supports that?
If sales material says a system reduces risk, where is the measurement?
If an investment firm says AI is part of its investment process, what exactly does the technology do?
A marketing compliance agent could identify claims involving performance, automation, intelligence, prediction or safety and require supporting evidence before publication.
That may sound small.
It can prevent a marketing sentence from becoming an enforcement exhibit.
Finding #3: The Most Valuable Compliance Database Will Connect Rules, Controls and Evidence
Most companies already have pieces of the information they need.
The problem is that the pieces live in different places.
The regulation is in one database.
The policy is in a document system.
The control is in a GRC platform.
The ticket is in a workflow tool.
The asset is in an IT system.
The log is in a security platform.
The vendor document is in procurement.
The approval is in email or chat.
The audit result is somewhere else.
An AI compliance agent becomes far more useful when it can navigate these relationships.
The Compliance Evidence Graph
A strong system should be able to answer:
RULE
↓
OBLIGATION
↓
POLICY
↓
CONTROL
↓
CONTROL OWNER
↓
SYSTEM / PROCESS
↓
EVIDENCE
↓
TEST RESULT
↓
EXCEPTION
↓
REMEDIATION
↓
APPROVAL
Every arrow matters.
If the regulation changes, the company can see which controls may be affected.
If a control fails, the company can see which obligations depend on it.
If an auditor asks for evidence, the company can follow the chain in reverse.
This is a more powerful model than storing thousands of documents in a searchable folder.
Which Compliance Workflows Should New York Companies Automate First?
Not every workflow deserves an agent.
NYC Tech Journal created a second scoring model to rank common compliance tasks.
We scored each workflow from one to five on five factors: volume, repeatability, ability to verify the answer, reversibility of mistakes, and ability to keep a human approval gate. The maximum score is 25.
Higher scores mean the task is better suited to early agent automation.
Chart 3: Compliance-Agent Automation Suitability
Regulatory change monitoring 24/25 ███████████████████
Evidence collection 24/25 ███████████████████
Policy-to-control mapping 23/25 ██████████████████
Vendor due diligence 22/25 █████████████████
Training / attestation tracking 21/25 ████████████████
Incident reporting preparation 21/25 ████████████████
Marketing claim review 20/25 ███████████████
AML alert investigation support 19/25 ██████████████
Hiring audit administration 18/25 █████████████
Final high-impact legal decisions 8/25 ██████
Again, this is NYC Tech Journal’s analytical framework, not a regulator-issued ranking.
Start With Regulatory Change Monitoring
This is usually a safer first agent because the system does not need authority to change the company.
It needs authority to watch, compare and prepare.
A useful output is not a 500-word summary.
It is a change package containing the original source, effective date, old language, new language, potentially affected controls, affected business units, recommended reviewers and required next actions.
Evidence Collection May Deliver Even Faster ROI
Evidence collection is repetitive, measurable and easy to audit.
The agent can retrieve information but does not have to make the final compliance decision.
This makes it a strong first deployment.
If the required artifact does not exist, the correct output is a gap.
That makes the agent easier to test.
Policy-to-Control Mapping Is the Foundation
A company cannot automate compliance effectively when no one knows which controls satisfy which obligations.
Agents can help build those connections.
But legal teams should approve important mappings before they become part of the trusted control library.
Once approved, the relationship can be reused every time a new audit, assessment or regulatory change arrives.
Vendor Due Diligence Has High Automation Potential
Most vendor reviews contain large amounts of repeated work.
Documents must be requested, read, compared, validated, renewed and escalated.
The agent can perform the first 70% of that workflow while humans concentrate on unusual or high-risk issues.
Final Decisions Should Stay Human
The lower end of the score is just as important.
An agent should not independently decide whether to file a suspicious activity report, terminate a customer, reject a loan, take adverse employment action, accept major cybersecurity risk, make a material securities disclosure or tell a regulator that the organization is compliant.
AI can prepare those decisions.
Accountable people should make them.
A Better Architecture for AI Compliance Agents
Buying an enterprise AI model is not the same as building a compliance system.
The architecture matters more than the chatbot.
Layer 1: Trusted Regulatory Sources
The agent should begin with an approved source registry.
For a New York financial company, that may include DFS, SEC, FINRA, FinCEN, OFAC, federal regulations, relevant New York statutes and carefully approved legal updates.
Public web search can help with discovery.
It should not silently become the source of truth.
Layer 2: Versioned Regulatory Documents
Every important source should have a version.
The company needs to know what language was in force when a decision was made.
Without version control, an AI system may answer a historical question using today’s rule.
That can become a serious audit problem.
Layer 3: Structured Obligations
The agent should convert text into small units of compliance work.
Each obligation should include scope, trigger, owner, frequency, required evidence, related controls and source citation.
Humans approve high-impact interpretations.
Layer 4: Internal Control Library
Every obligation should map to one or more controls.
Controls need owners, procedures, testing methods and expected evidence.
This layer turns legal requirements into something the business can actually execute.
Layer 5: Evidence Connectors
The agent should connect only to systems it needs.
That may include identity systems, ticketing software, policy repositories, HR systems, asset inventories, vendor platforms, security tools or transaction-monitoring systems.
Read-only access should be the default wherever possible.
Layer 6: Approval and Action
The agent should know what it can do by itself.
It should also know what requires approval.
| Action | Suggested permission |
| Read public regulation | Automatic |
| Compare two rule versions | Automatic |
| Search approved policies | Automatic |
| Collect evidence | Automatic or controlled |
| Create compliance ticket | Usually automatic |
| Recommend policy change | Draft only |
| Approve control effectiveness | Human |
| Accept material risk | Human |
| Send material regulator filing | Human approval |
| Change customer status | Human-controlled |
| Change production security controls | Strict approval |
Layer 7: Immutable Audit Trail
Every important action should be recorded.
The log should show the input, source, model or agent version, tools accessed, data retrieved, conclusion, confidence, approval status, reviewer and final action.
If an agent can act but nobody can reconstruct what it did, it does not belong in a mature compliance environment.
Agent Identity Will Become a Compliance Control
Companies already manage human identities.
They know which employee can access which system.
Agents need the same treatment.
An agent should have a named identity, defined role, approved systems, data permissions, spending or action limits, review owner and kill switch.
This is especially important because agents can operate faster than people.
A human employee might make three bad decisions before a manager notices.
An automated process can make thousands.
The solution is not to avoid agents.
The solution is to reduce their authority.
Human-in-the-Loop Is Too Vague
Many AI governance plans say there will be a “human in the loop.”
That sounds safe but often explains very little.
Which human?
At what point?
What information do they see?
Can they reject the recommendation?
Are they expected to review every case or only exceptions?
How long do they have?
What happens if nobody responds?
The approval design needs to be specific.
Use Different Human Gates for Different Risk Levels
| Risk level | Example | Human model |
| Low | Regulatory news classification | Review by exception |
| Moderate | Vendor risk score | Human approval before onboarding |
| High | Regulatory filing draft | Qualified reviewer signs off |
| Very high | Customer termination or major risk acceptance | Senior accountable decision-maker |
This also prevents a hidden problem.
If humans approve 1,000 AI decisions every day, there is not meaningful oversight.
There is rubber stamping.
The KPI Dashboard Every Compliance-Agent Program Should Build
Companies should not judge their compliance agent by how impressive its answers sound.
Measure the operating system.
Compliance Agent KPI Dashboard
| KPI | What it tells you |
| Regulatory change detection rate | Whether important changes are being captured |
| False regulatory alerts | Whether monitoring creates noise |
| Source citation accuracy | Whether conclusions point to the correct authority |
| Obligation-mapping accuracy | Whether rules are mapped to the right controls |
| Evidence retrieval success | Whether required proof can actually be found |
| Unsupported conclusion rate | How often the agent states something without enough evidence |
| Human override rate | Whether reviewers regularly disagree |
| Exception aging | How long unresolved gaps remain open |
| Permission violations | Whether agents attempt unauthorized actions |
| Stale evidence rate | Whether control proof is still current |
| Time to regulatory impact assessment | Speed from publication to internal review |
| Audit preparation hours | Whether automation reduces manual evidence work |
One KPI deserves special attention: unsupported conclusion rate.
A compliance agent should be rewarded for refusing to make claims when evidence is missing.
That is the opposite of many consumer AI systems, where producing an answer feels like success.
In compliance, sometimes the best answer is “not proven.”
A Practical 90-Day Compliance-Agent Plan
Trying to automate an entire compliance department at once is a bad starting point.
A better approach is to build one narrow workflow and prove that the system is more reliable than the process it replaces.
Days 1–30: Build the Control Foundation
The first month should focus on information rather than autonomy.
Choose one regulatory area. Cybersecurity, vendor risk or regulatory change monitoring are good examples.
Identify the authoritative regulatory sources. Build an approved obligation list. Map each obligation to internal policies and controls. Define which evidence proves each control. Assign an owner.
The company should also create an AI agent access policy.
Decide which systems the agent may read, which information it may store, which actions it may take, and which actions always require approval.
Days 31–60: Run the Agent in Shadow Mode
Do not let the agent run the process yet.
Let it observe the same work humans are doing.
If compliance analysts review regulatory updates, let the agent independently review them too.
Compare the results.
If analysts collect 50 pieces of audit evidence, ask the agent to collect the same 50.
Measure how many are correct.
Track omissions.
Track false positives.
Track source errors.
Track stale documents.
This is how trust is earned.
Days 61–90: Automate the Low-Risk Steps
Once accuracy is acceptable, allow the agent to take narrow actions.
It might automatically create a ticket when a regulatory change is detected.
It might request missing evidence from a control owner.
It might remind a vendor owner when a review is approaching expiration.
It might create a draft regulatory impact assessment.
Humans still approve the high-impact result.
Table: 90-Day Rollout
| Period | Main goal | Agent authority |
| Days 1–30 | Build sources, controls and evidence map | Read only |
| Days 31–60 | Test against human process | Shadow mode |
| Days 61–90 | Automate repeatable steps | Limited actions |
| After 90 days | Expand based on measured reliability | Risk-based permissions |
How Banks and Fintech Companies Should Use Compliance Agents
Financial firms should begin where volume is high and decisions can still be reviewed.
AML investigation support is an obvious example.
An agent can collect customer information, summarize transaction history, build timelines, identify linked accounts, search prior alerts and prepare an investigation file.
It can reduce the amount of time analysts spend moving between systems.
But the firm should be careful with the final judgment.
The Block and Paxos matters show why. DFS focused on problems involving customer due diligence, monitoring, illicit activity, alert backlogs, partner oversight and escalation. (Department of Financial Services)
Automating a weak process simply makes the weakness faster.
The better strategy is to give AI the job of finding evidence and surfacing anomalies while keeping regulated judgment under controlled human ownership.
How Insurers Should Use Compliance Agents
Insurance companies face a different opportunity.
They often manage many models, external data sources, underwriting rules and vendor systems.
An agent can maintain the model inventory, track testing schedules, compare model versions, collect fairness assessments, record data sources and watch for material changes.
It can also create a much stronger examination file.
Instead of rebuilding an AI governance history when DFS asks questions, the company already has a continuous record.
That is the real advantage.
The system is not helping the company “pass an audit.”
It is making the company auditable every day.
How Large NYC Employers Should Use Compliance Agents
Employers should focus on system inventory first.
A company may think it uses one AI hiring tool while AI features are embedded inside several recruiting, assessment and applicant-tracking platforms.
The compliance agent can maintain a registry of systems that influence hiring.
For each tool, it can track whether it falls within the company’s interpretation of applicable rules, the date of the last review, vendor changes, audit status, candidate notice requirements and public disclosure status.
The human legal team determines scope.
The agent makes sure the conclusion does not disappear inside an old spreadsheet.
How Public Companies Should Use Compliance Agents
Public companies can use agents to connect cybersecurity operations with disclosure processes.
SEC rules require public companies to disclose material cybersecurity incidents on Form 8-K generally within four business days after determining that an incident is material. Companies must also provide annual information about cybersecurity risk-management, strategy and governance processes. (SEC)
An agent can help build the information flow needed before the materiality decision.
It can assemble incident facts, identify affected systems, connect the incident with prior risk assessments, track investigation status and prepare a structured package for legal and disclosure committees.
It should not decide materiality on its own.
Speed is useful.
Uncontrolled legal judgment is not.
Compliance Agents Should Reduce Alert Backlogs, Not Create New Ones
One of the easiest ways to ruin an AI compliance program is to generate thousands of low-value alerts.
Traditional compliance systems already suffer from this problem.
AI can make it worse.
If a regulatory agent flags every paragraph change as material, employees will stop paying attention.
If a vendor agent produces 40 warnings for every supplier, reviewers will click through them.
If a transaction agent describes everything as suspicious, analysts cannot find the real problems.
Agents need prioritization.
A useful regulatory alert might combine four factors: whether the company is in scope, whether the requirement changed, how many internal controls are affected and how severe the possible impact is.
That allows the system to say:
“This update contains 37 text changes, but only three appear to affect existing obligations. Two controls require review within 30 days.”
That is useful.
A 20-page summary is not.
Finding #4: Risk Assessment Is Becoming a Living System
One of the strongest signals from the New York research is the movement away from annual compliance exercises.
DFS’s newest risk-assessment guidance says assessments should be updated at least annually but also when material business or technology changes affect risk. It describes strong assessments as dynamic, data-driven and connected with governance, controls and remediation. (Department of Financial Services)
Agents make that model much easier to operate.
The risk register no longer has to wait for next quarter’s meeting.
A major vendor change can update exposure.
A new AI deployment can open a review.
A security incident can change the probability score.
A completed remediation ticket can reduce residual risk.
A regulatory update can create a new obligation.
This turns risk assessment from a document into a system.
The Biggest Mistake Will Be Letting the Agent Approve Its Own Work
Suppose an agent interprets a requirement.
It maps the requirement to a control.
It tests the control.
It decides the control passed.
It closes the exception.
It generates the certification.
Nothing in that chain is independent.
The system has effectively audited itself.
That is dangerous even if the model is very accurate.
Companies should separate agent roles just as they separate important human responsibilities.
One agent can collect evidence.
Another system can test deterministic conditions.
A qualified person can approve the conclusion.
Internal audit can independently inspect the process.
The goal is controlled automation, not maximum automation.
NIST Gives Companies a Useful Structure Even When It Is Not the Law
Companies do not need to invent every AI governance idea themselves.
The NIST AI Risk Management Framework organizes AI risk work around four main functions: Govern, Map, Measure and Manage. NIST describes the framework as voluntary and emphasizes continuous risk management, documentation, testing and measurement. (NIST)
Its Generative AI Profile adds guidance aimed specifically at generative systems, including provenance, testing, feedback, third-party relationships and emerging risks. (NIST)
A New York company can use that structure to organize internal AI controls even when the specific NIST action is not legally required.
The important point is to label the source correctly.
A compliance agent should know the difference between:
“This is required by law.”
“This is regulator guidance.”
“This is a company policy.”
“This is a voluntary framework.”
“This is an AI recommendation.”
If those categories become mixed together, the compliance system becomes unreliable.
New York State Is Using AI for Regulatory Work Too
There is another signal worth watching.
In July 2026, Governor Kathy Hochul announced a statewide “Regulatory Reset” aimed at reviewing large numbers of regulations and laws for possible modernization. The state said it was working with outside organizations to use AI-enabled tools to speed the initial review while keeping human safeguards. (Governor Kathy Hochul)
That does not mean regulators will suddenly automate enforcement.
It does suggest that machine-assisted regulatory analysis is moving to both sides of the table.
Companies may use AI to understand regulators.
Regulators may use AI to review rules, data, filings and regulated firms.
That will place even more value on structured, accurate and machine-readable compliance evidence.
What the Economics of Compliance Agents Should Look Like
Companies should be skeptical of vague claims that AI will reduce compliance cost by 70% or replace entire departments.
The better business case is built workflow by workflow.
Take regulatory change management.
Measure how many regulatory updates the team reviews each month. Calculate analyst hours spent reading, routing and mapping them. Measure how many turn out to be irrelevant. Measure the average time between publication and internal assignment.
Then run the agent.
Do the same for evidence gathering, vendor review or alert investigations.
A Simple ROI Model
| Input | Example measure |
| Annual workflow volume | 10,000 reviews |
| Current minutes per item | 20 minutes |
| Loaded employee cost | Cost per working hour |
| Agent-assisted minutes | 8 minutes |
| Human-review requirement | Percentage still reviewed |
| Technology cost | Annual system cost |
| Error remediation cost | Cost of incorrect outputs |
| Audit savings | Reduction in preparation time |
The business case should include errors.
If the agent saves 10,000 hours but creates serious compliance failures, there is no ROI.
The correct formula is closer to:
Labor savings + faster response + lower audit cost + reduced backlog − technology cost − oversight cost − error cost − new AI risk.
That is a much harder calculation.
It is also more credible.
The Firms That Win Will Automate Preparation Before Judgment
Compliance professionals spend a surprising amount of time preparing to think.
They search.
They gather.
They format.
They compare.
They copy information between systems.
They chase evidence.
They prepare meeting packets.
They rebuild histories.
Those steps are where agents can create large value without taking away human accountability.
A compliance officer should spend more time deciding whether a risk is acceptable.
They should spend less time locating the spreadsheet containing the evidence.
Five Predictions for New York’s Compliance-Agent Era
Compliance Will Become More Event-Driven
Annual reviews will remain because many rules require them.
But agents will make it practical to review risks when important events happen.
A new vendor, system, regulation, model version, incident or business acquisition can automatically start the correct compliance workflow.
Evidence Graphs Will Matter More Than Chatbots
The interface will become less important.
The valuable asset will be the structured map connecting rules, obligations, policies, controls, systems and evidence.
Once that graph exists, many different AI systems can work on top of it.
Agent Permissions Will Become Part of the Audit
Auditors will increasingly want to understand what automated systems were allowed to do.
Companies will need records of agent identities, permissions, approvals, actions and changes.
“AI governance” will become part of normal access governance.
Compliance Logs Will Become Easier for Regulators to Read
Companies have historically prepared examination evidence after receiving a request.
Continuous compliance systems can make much of that evidence available in structured form from the start.
That could reduce preparation time while making weak controls easier to discover.
Human Compliance Work Will Move Toward Exceptions
The job will not disappear.
It will move.
People will spend less time on normal cases and more time on unusual cases, conflicting evidence, new regulations, difficult interpretations and risk decisions.
That is where experienced judgment creates the most value.
What New York Business Leaders Should Do Now
The first step is not buying an AI compliance platform.
The first step is identifying one compliance workflow that is expensive because information has to move through many systems.
Map the workflow from start to finish.
Identify the authoritative source.
Define every important decision.
Define what evidence proves each step.
Decide which actions can be reversed.
Decide which actions require human approval.
Then test an agent against the current human process.
That approach is slower than giving an AI model broad access on day one.
It is much faster than cleaning up a compliance failure later.
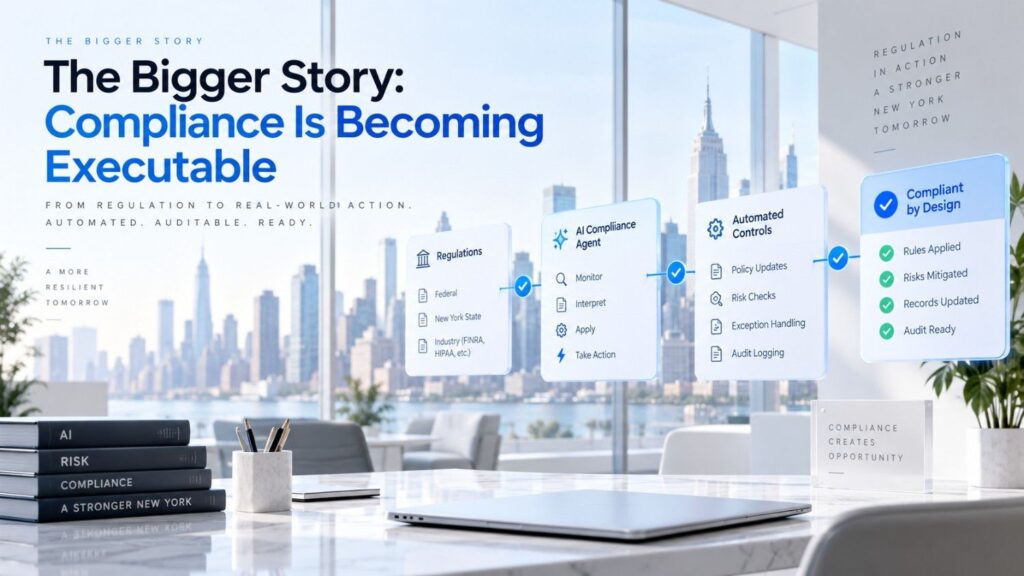
The Bigger Story: Compliance Is Becoming Executable
The most important change is not that AI can read regulations.
Search engines could already find rules, and lawyers could already interpret them.
The bigger change is that software can increasingly connect regulatory language with actual business processes.
A requirement can become a control.
A control can be linked to evidence.
Missing evidence can become an exception.
An exception can become a remediation task.
A material change can start a new assessment.
A deadline can create an escalation.
A regulator request can produce a complete evidence package.
That is what makes compliance agents different.
Our review of 15 public regulatory and risk-management sources found that testing, reporting, documentation, inventory and monitoring appeared again and again. Our separate review of 13 company-level DFS matters found nearly $89.7 million in clearly attributable penalties in the selected 2025 cases, with cybersecurity dominating the number of entities while AML failures dominated penalty dollars.
The lesson from both datasets is similar.
Regulators are not simply asking whether a company has policies.
They want systems that identify risk, test controls, preserve evidence, detect problems, escalate them and prove that responsible people acted.
AI agents can help build that system.
But the winning model will not be an autonomous compliance officer that replaces human judgment.
It will be a tightly controlled network of agents that does the repetitive work around judgment: watching, gathering, mapping, checking, documenting and escalating.
For New York companies, that may be the real promise of agentic compliance.
Not compliance without people.
Compliance that is finally able to keep up.
Sources
The original analysis above primarily used official materials from the New York City Department of Consumer and Worker Protection and New York State Comptroller on Local Law 144; New York DFS cybersecurity, AI, insurance, third-party and enforcement materials; New York legislation and Governor’s Office materials covering frontier AI; SEC cybersecurity and AI-enforcement materials; FINRA GenAI and agent guidance; FTC enforcement material; and the NIST AI Risk Management Framework and Generative AI Profile. (Office of the State Comptroller)
The enforcement calculations are NYC Tech Journal’s own analysis of disclosed figures and classifications from DFS’s 2025 annual enforcement report. The $89.665 million figure is intentionally a selected-sample total rather than a claim about all DFS enforcement during 2025; multistate matters without a clearly attributable New York amount were excluded from that calculation. (Department of Financial Services)